Build secure REST APIs with authentication, rate limiting, and instant documentation
Deploy production-ready APIs in minutes with built-in auth, intelligent rate limiting, and auto-generated OpenAPI specs. Focus on your logic, we handle the infrastructure.
Trusted by leading development teams
Everything you need to ship secure APIs
JWT tokens, OAuth 2.0, and API key management out of the box. Role-based access control lets you define granular permissions per endpoint. Rotate credentials, revoke access, and audit every request without writing a single line of auth logic.
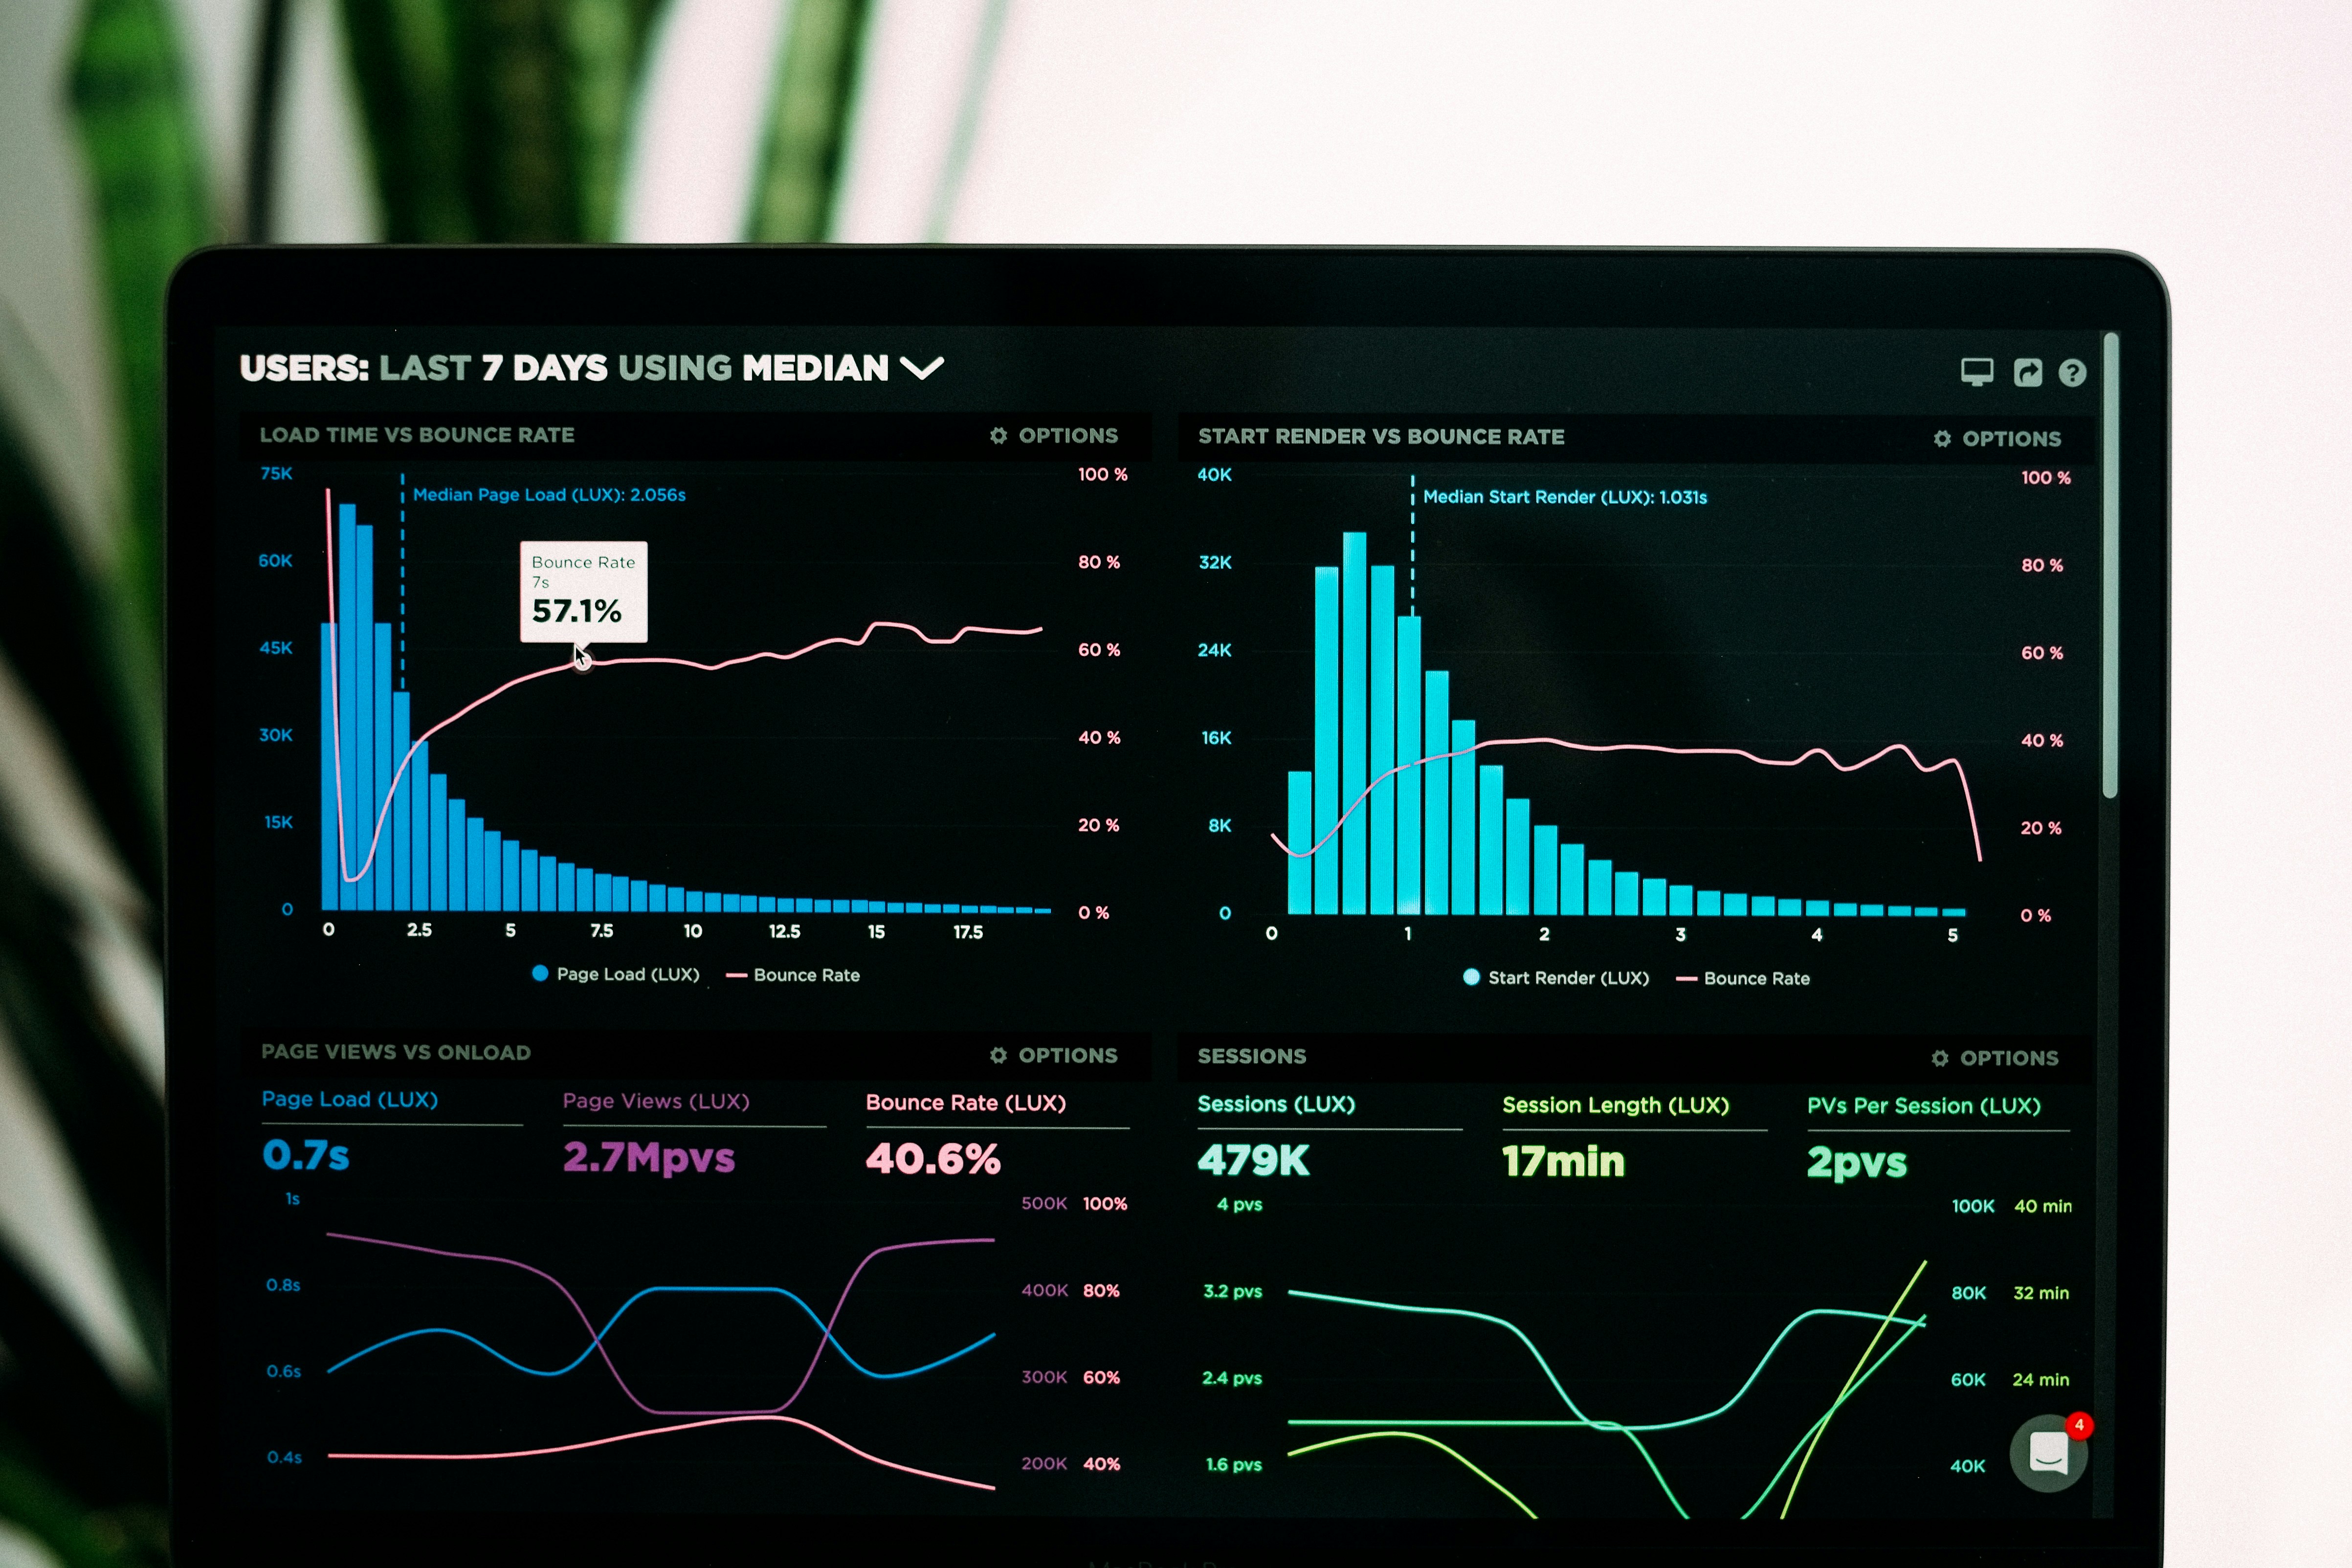
Protect your infrastructure with per-key, per-endpoint, or global rate limits. Sliding windows, token buckets, and custom quotas adapt to your traffic patterns. Real-time dashboards show who's hitting limits and when, so you can scale proactively.
Your API spec writes itself from route definitions and type annotations. Interactive docs let developers test endpoints in the browser, see live examples, and download SDKs in eight languages. One source of truth, always in sync.
import { Gateway } from '@apigateway/sdk'; const gateway = new Gateway({ apiKey: process.env.GATEWAY_KEY, rateLimit: { requests: 1000, window: '1h' } }); gateway.post('/users', async (req, res) => { // Auth, validation, and rate limiting handled const user = await db.users.create(req.body); res.json(user); }); // OpenAPI spec auto-generated at /docs gateway.listen(3000);Deep dive
Rate limits that think ahead
Define thresholds once — per API key, per endpoint, or globally — and the gateway enforces them in real time. Traffic spikes trigger alerts before limits break. Burst allowances let legitimate clients recover gracefully, while bad actors hit the wall instantly. Every throttle event lands in the audit log with client ID, timestamp, and retry-after headers.
- 1Per-key quotas reset on a sliding window, not midnight
- 2Burst allowance: 20% over limit for 10 seconds
- 3Real-time alerts when any key hits 80% of quota
- 4Audit log captures every throttled request with retry-after
Connects to the tools you already use
Not just webhooks — here's what each integration actually unlocks.
Datadog
Every API call becomes a trace — latency, errors, and rate-limit hits stream to your existing dashboards.
PagerDuty
Rate-limit breaches and auth failures trigger incidents automatically, with full context for on-call engineers.
GitHub
OpenAPI specs commit to your repo on every deploy, so docs and code stay in lockstep.
Postman
Collections sync from your live spec — teammates always test against the current endpoints.
Terraform
Provision gateways, keys, and rate limits as code — no clicking through dashboards to replicate environments.
Webhooks
Push auth events, quota warnings, and usage summaries to any service that speaks HTTP.
From first request to production in four screens
The workflow you'll use every day, start to finish.
Built for scale and reliability
What developers are saying
We went from two weeks of auth boilerplate to production in an afternoon. The auto-generated docs saved us another sprint of Swagger wrangling.
Rate limiting used to mean Redis clusters and late-night pages. Now it's three lines of config and we sleep through the night.
Our API docs were always six commits behind. With API Gateway they update on deploy and our support tickets dropped by half.
Ship secure APIs today
Start with our free tier — 100,000 requests per month, full auth and rate limiting, and auto-generated docs. No credit card required. Upgrade when you're ready to scale.