Enterprise-grade API infrastructure, zero configuration
Everything you need to ship production APIs

Built-in authentication
OAuth 2.0, JWT, and API key authentication work out of the box. No middleware to configure, no security vulnerabilities to patch. Rotate keys, revoke tokens, and audit access from a single dashboard.
Intelligent rate limiting
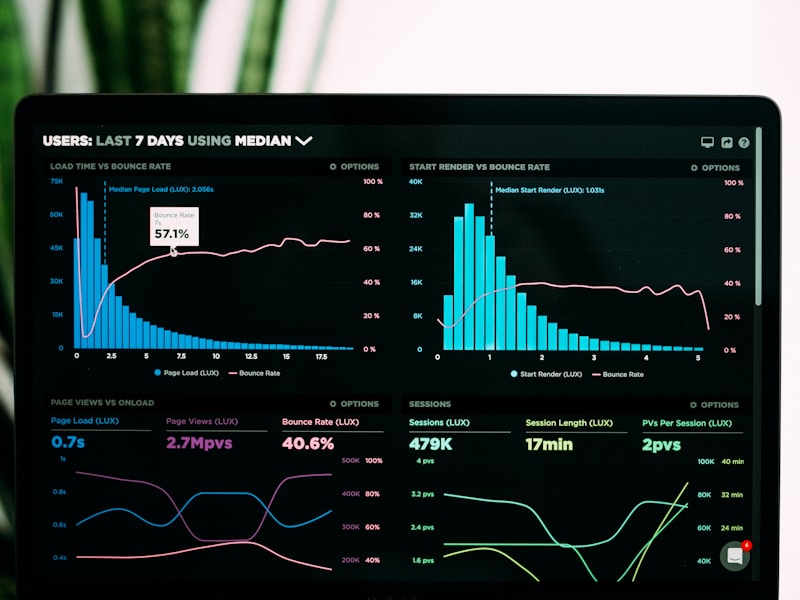
Per-user, per-endpoint, and global rate limits prevent abuse without blocking legitimate traffic. Sliding window algorithms ensure fair usage. Configure limits in seconds, enforce them at the edge.

Auto-generated OpenAPI docs
Interactive API documentation updates automatically from your code. Test endpoints, explore schemas, and generate client SDKs without writing a single line of YAML. Always in sync, never out of date.
Request validation
Schema-based validation catches malformed requests before they reach your application. JSON Schema, XML, and custom validators protect your endpoints from bad data and injection attacks.
Real-time monitoring
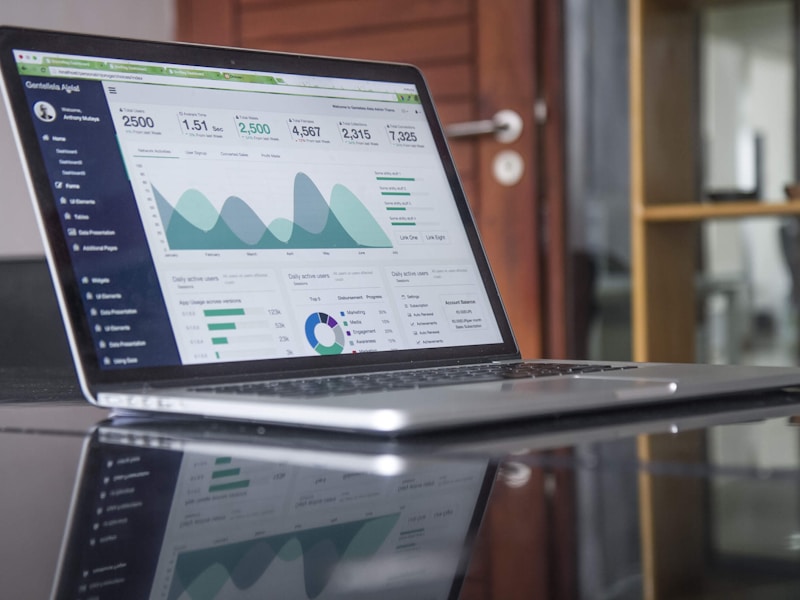
Track latency, error rates, and throughput across every endpoint. Distributed tracing shows you exactly where requests slow down. Set alerts for anomalies and get notified before users complain.

Version management
Deploy multiple API versions simultaneously without breaking existing clients. Route traffic by header, query parameter, or subdomain. Deprecate old versions gracefully with automatic migration warnings.
Integrate in minutes, not days
import { Gateway } from '@apigateway/node'; const gateway = new Gateway({ apiKey: process.env.GATEWAY_KEY }); gateway.route('/users/:id', { auth: 'jwt', rateLimit: { requests: 100, window: '1m' }, handler: async (req) => { return db.users.findById(req.params.id); } }); gateway.listen(3000);from apigateway import Gateway, RateLimit gateway = Gateway(api_key=os.getenv('GATEWAY_KEY')) @gateway.route('/users/<id>', auth='jwt') @RateLimit(requests=100, window='1m') async def get_user(id: str): return await db.users.find_by_id(id) if __name__ == '__main__': gateway.run(port=3000)package main import ( "github.com/apigateway/go-sdk" ) func main() { gw := gateway.New(gateway.Config{ APIKey: os.Getenv("GATEWAY_KEY"), }) gw.Route("/users/:id", gateway.Options{ Auth: gateway.JWT, RateLimit: &gateway.RateLimit{ Requests: 100, Window: "1m", }, Handler: getUserHandler, }) gw.Listen(":3000") }# Create an API endpoint curl -X POST https://api.gateway.dev/v1/routes \ -H "Authorization: Bearer $GATEWAY_KEY" \ -H "Content-Type: application/json" \ -d '{ "path": "/users/:id", "auth": "jwt", "rateLimit": { "requests": 100, "window": "1m" }, "upstream": "https://your-api.com" }'resource "apigateway_route" "get_user" { path = "/users/:id" method = "GET" auth { type = "jwt" issuer = "https://auth.example.com" } rate_limit { requests = 100 window = "1m" } upstream { url = "https://your-api.com" timeout = "30s" } }version: '3.8' services: gateway: image: apigateway/gateway:latest ports: - "3000:3000" environment: - GATEWAY_KEY=${GATEWAY_KEY} - AUTH_PROVIDER=jwt - RATE_LIMIT_REQUESTS=100 - RATE_LIMIT_WINDOW=1m volumes: - ./config.yml:/etc/gateway/config.yml command: gateway serveUnder the hood
The architecture that keeps your APIs fast and secure
Edge-first routing
Every request hits our global edge network first. TLS termination, DDoS protection, and geo-routing happen in under 5ms. Your origin servers only see validated, authenticated traffic.
Zero-copy authentication
JWT validation and API key lookups run in-memory at the edge. No database round-trips, no Redis calls. Sub-millisecond auth checks mean your p99 latency stays under 50ms globally.
Distributed rate limiting
Rate limit counters sync across regions using CRDTs. No central bottleneck, no race conditions. A user hitting Tokyo and London simultaneously gets accurate, fair limits without coordination overhead.
Schema-driven validation
Request validation compiles your OpenAPI schemas to native code. Malformed JSON, missing fields, and type errors fail in microseconds. Invalid requests never touch your application logic.
Observability by default
Distributed tracing headers propagate automatically. Every request gets a trace ID, every hop records timing. Correlate logs, metrics, and traces without instrumenting a single line of code.
Graceful degradation
Circuit breakers detect failing upstreams and shed load automatically. Fallback responses keep clients happy while your services recover. No cascading failures, no thundering herds.
Request path
From request to response in milliseconds
- 01
Define your routes
Declare endpoints in code, config files, or our web UI. Specify authentication requirements, rate limits, and validation rules. Changes deploy globally in under 60 seconds.
- 02
Generate API keys
Create API keys for your services or issue JWT tokens for users. Set expiration dates, scope permissions, and usage quotas. Rotate credentials without downtime.
- 03
Configure rate limits
Set per-user, per-endpoint, or global rate limits. Choose between fixed window, sliding window, or token bucket algorithms. Override limits for premium tiers or internal services.
- 04
Deploy and monitor
Push changes to production with zero downtime. Watch real-time metrics for latency, throughput, and errors. Set alerts for anomalies and get notified via Slack, PagerDuty, or webhooks.